I get FOMO when looking at the promised productivity gains from all these amazing-looking new platforms I hear about every week (each bearing enticing promises of automating this or that generic administrative task), but I find myself regularly holding back from using them against the backdrop of not opening myself up to unreasonable security and privacy risk.
Here’s a practical example of how I did a 30 second risk sanity check for one I was about to try out earlier today that wanted access to my inbox, which is a big red flag for me:
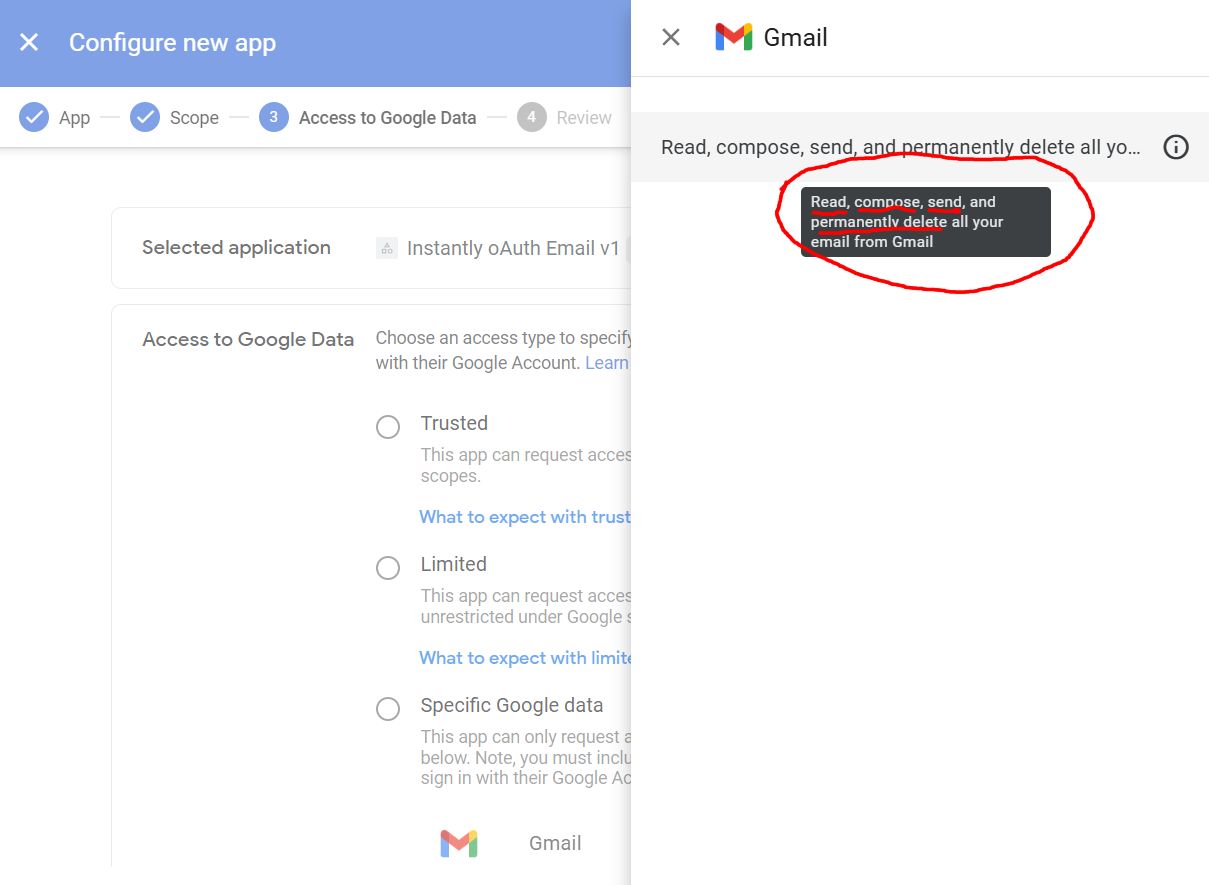
Step 1. Find out what permissions they are requesting When clicking through the sign-up/onboarding process, you’ll eventually get to a screen where you are redirected to a Google / MSFT “Permissions Requested” screen, where you can see what accesses they are requesting. Screenshot these permissions, so you can use it in Step 2.
Step 2. Sanity Check with some research Ask an LLM to do a little bit of research for you (use one of the multi-step models that make web calls like “Gemini Pro 2.5” or “ChatGPT 4o” or “ChatGPT 5”):
— Begin Prompt — I want to understand how likely the product company at https://companyname.com to be a security/privacy risk if I link my Google Account, providing access them to the permissions requested in this screenshot. (In this case it was “Create, Read, Update and Delete data from my inbox”).
Research any publicly published information about their security/privacy compliance processes that have been audited by a third party (such as ISO27k, SOC2, or Security Penetration Test outcomes).
I’m looking for a specific assessment based on the age, size and likely maturity of this company in particular, not a general assessment of the risks associated with the known high risk activity of sharing broad administrative access to my inbox (as I already know this is considered high risk).
Provide me a Risk Rating of Red/Amber/Green for how I should understand this risk were I to adopt this product and provide it the permissions requested. — End Prompt —
The prompt came back that the vendor was 3 years old, had ~130 employees, and had no publicly published information on independent verification of their security/privacy practices, and strongly cautioned me against using the product until I had asked the vendor to explicitly provide some independent verification that they were taking suitable steps to protect their systems.
Honestly, it was good advice.
Can I rely on an LLM providing sensible advice? No.
Is this approach sufficient for larger organisations with mature Sec/Priv functions? No.
Is performing a basic step like this much better than going in blind? Sure is.
People that currently blindly click “I accept”, you know who you are. This post is for you.